Code assurance for the AI era
From code risk to team action.
A report is a starting point, not the finish line. Bring repository health, remediation ownership and risk decisions into the same workflow as AI-assisted development.
MCP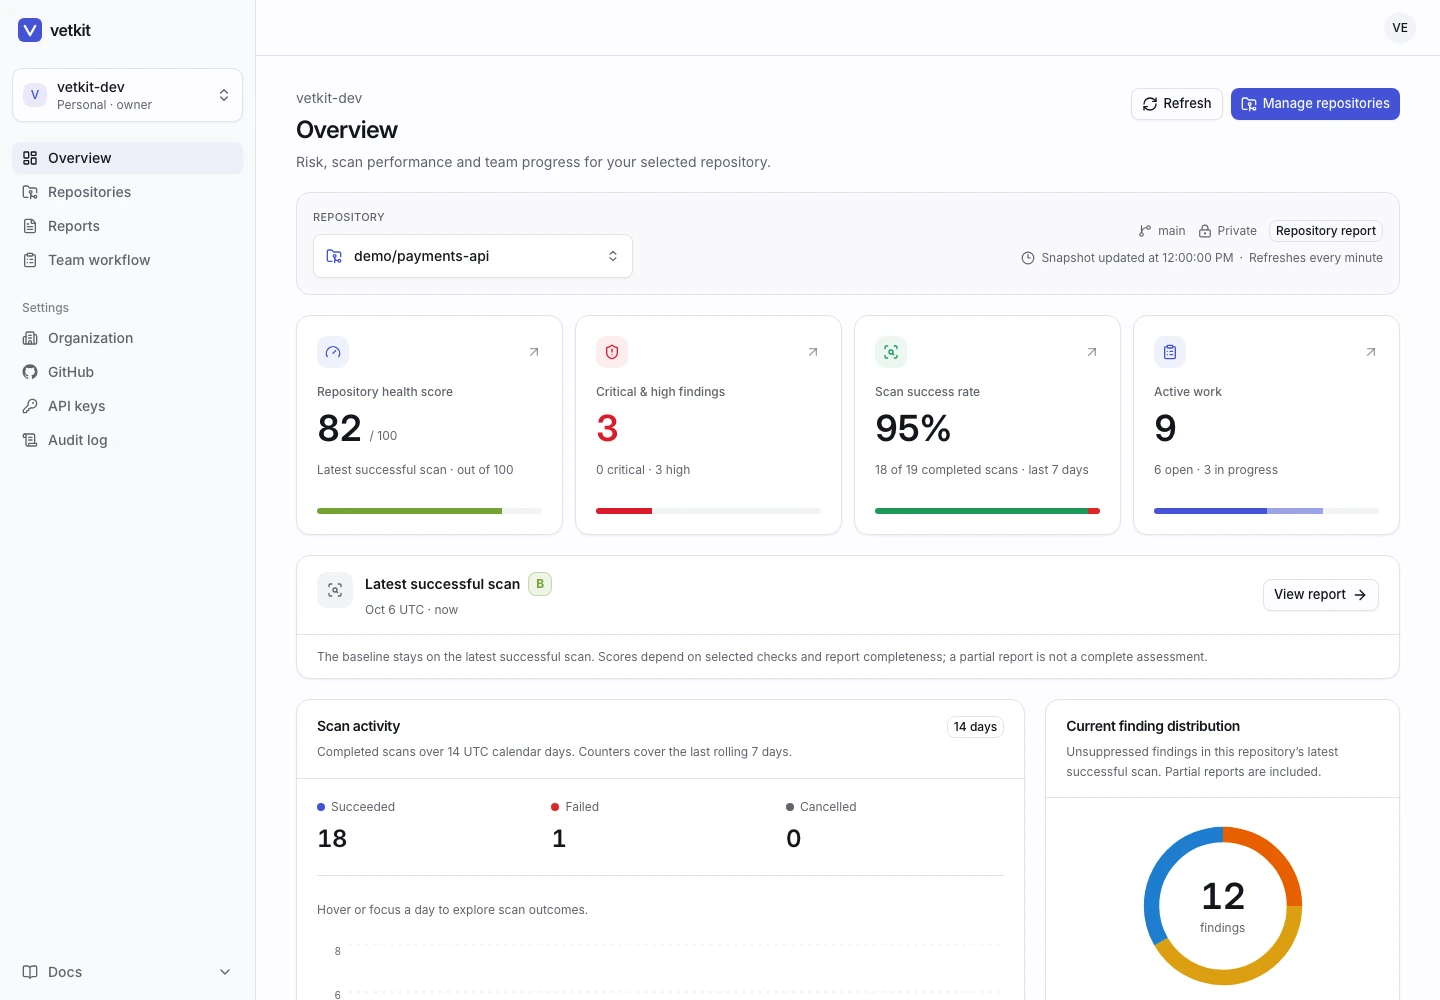
Platform overview · Free Quick Scan includes only secrets, known dependency vulnerabilities and basic security posture. Expanded checks and automation belong to the Full tier; paid plans are not yet available for purchase.
Know where your code stands
Repository health, high-priority findings, scan activity and remediation work — in one clear view for your selected repository.
Switch between connected repositories to review their latest successful scans, overdue work and pending risk decisions. Partial reports and stale scans are labelled; missing scan evidence is not evidence of safety.
Give every fix an owner
Assign findings, set priorities and target dates, discuss progress and follow open, in-progress and resolved work.
Ownership and discussion follow the same finding across later audits. Risk acceptance and false-positive decisions require a reason and independent administrator review in team organizations. Accepted risks expire; marking work resolved does not verify a fix or suppress a finding.
Close the AI development loop
Connect coding agents through MCP, run audits through the REST API and bring actionable findings back into development.
Check hallucinated packages, unfinished implementations, LLM security patterns and production pitfalls. Optional AI review uses your provider key and explicit consent to review a source sample. It is advisory, not a scored scan, and is not included in Free Quick Scan.
MCPMake decisions with evidence
File-and-line findings, severity, tool versions, grades and audit comparisons — not another unexplained AI verdict.
Export deterministic findings as SARIF, or share PDF, Markdown and JSON reports. Compare scans to see new and fixed findings. Selected checks define the report's coverage; a good grade is not a security certification or a guarantee of production readiness.
REST APIFor the people accountable for shipping
Founders & builders
Get a second look at AI-built code before your next release, starting with a free security check.
Engineering teams
Keep risks, owners, deadlines and remediation progress visible across your repositories.
Technical leaders
Review scan coverage and outstanding work without treating commit counts or grades as developer productivity.
Get a second pair of eyes on your next release.
Sign in with GitHub, connect your repository and get your first security report. All detected findings stay visible — even the critical ones.
Prefer to write directly? contact@vetkit.dev