Skip to content
Free Security Quick Scan

Code moves fast. Risk stays visible.

Find code risks across popular programming languages, turn findings into team action, and re-scan to check fixes.

  • Read-only audit access
  • Your code is never executed
  • Secret values never stored
See supported languages & checks
app.vetkit.dev/dashboard
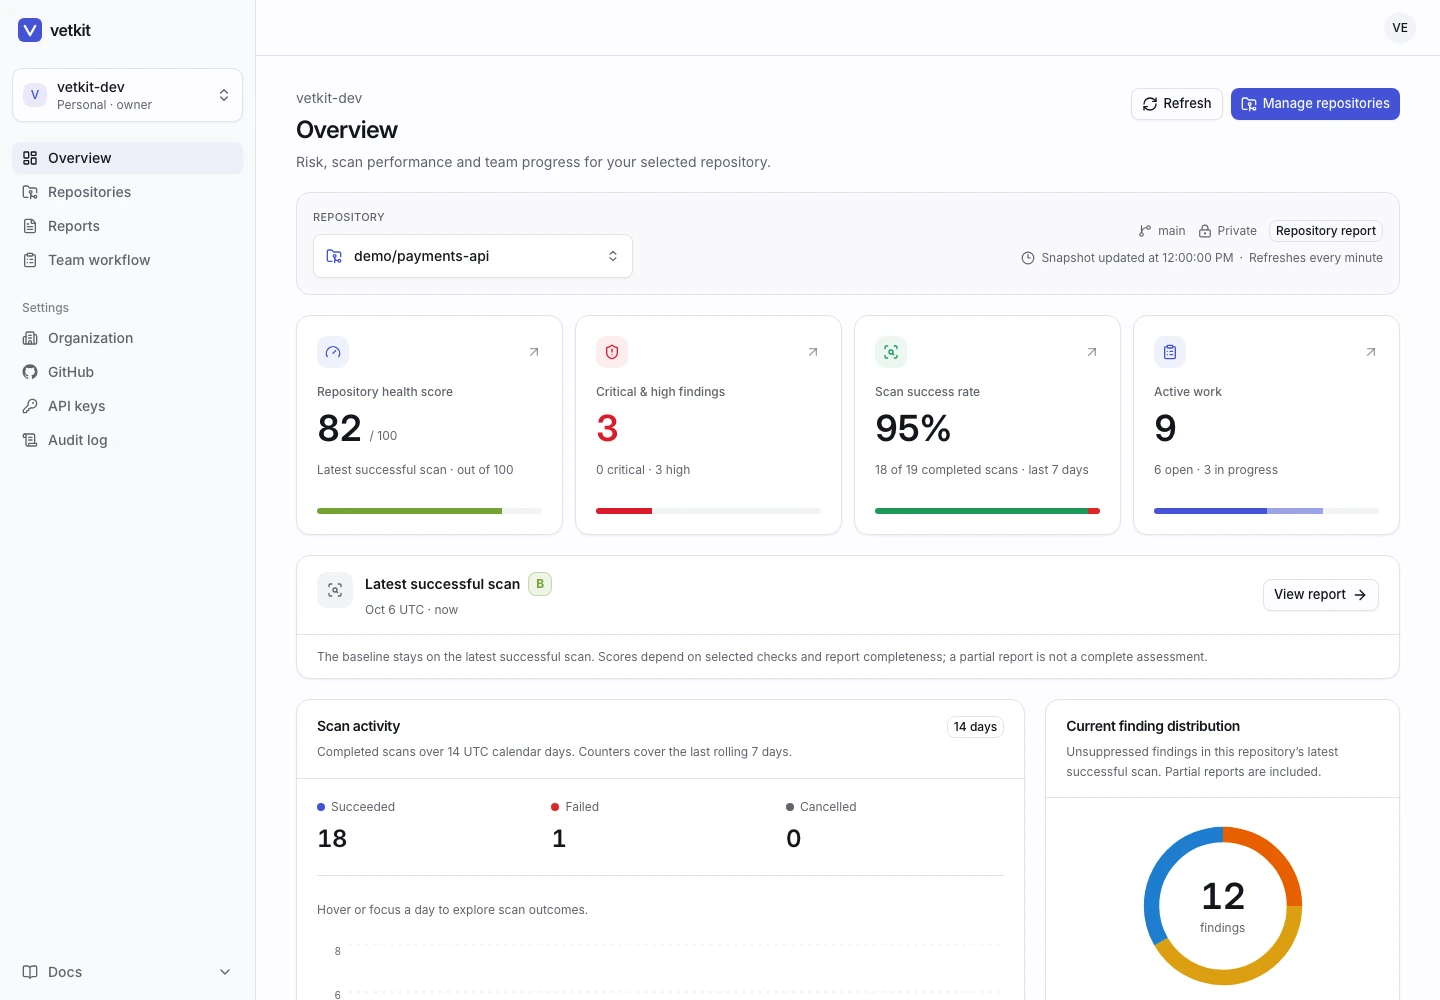
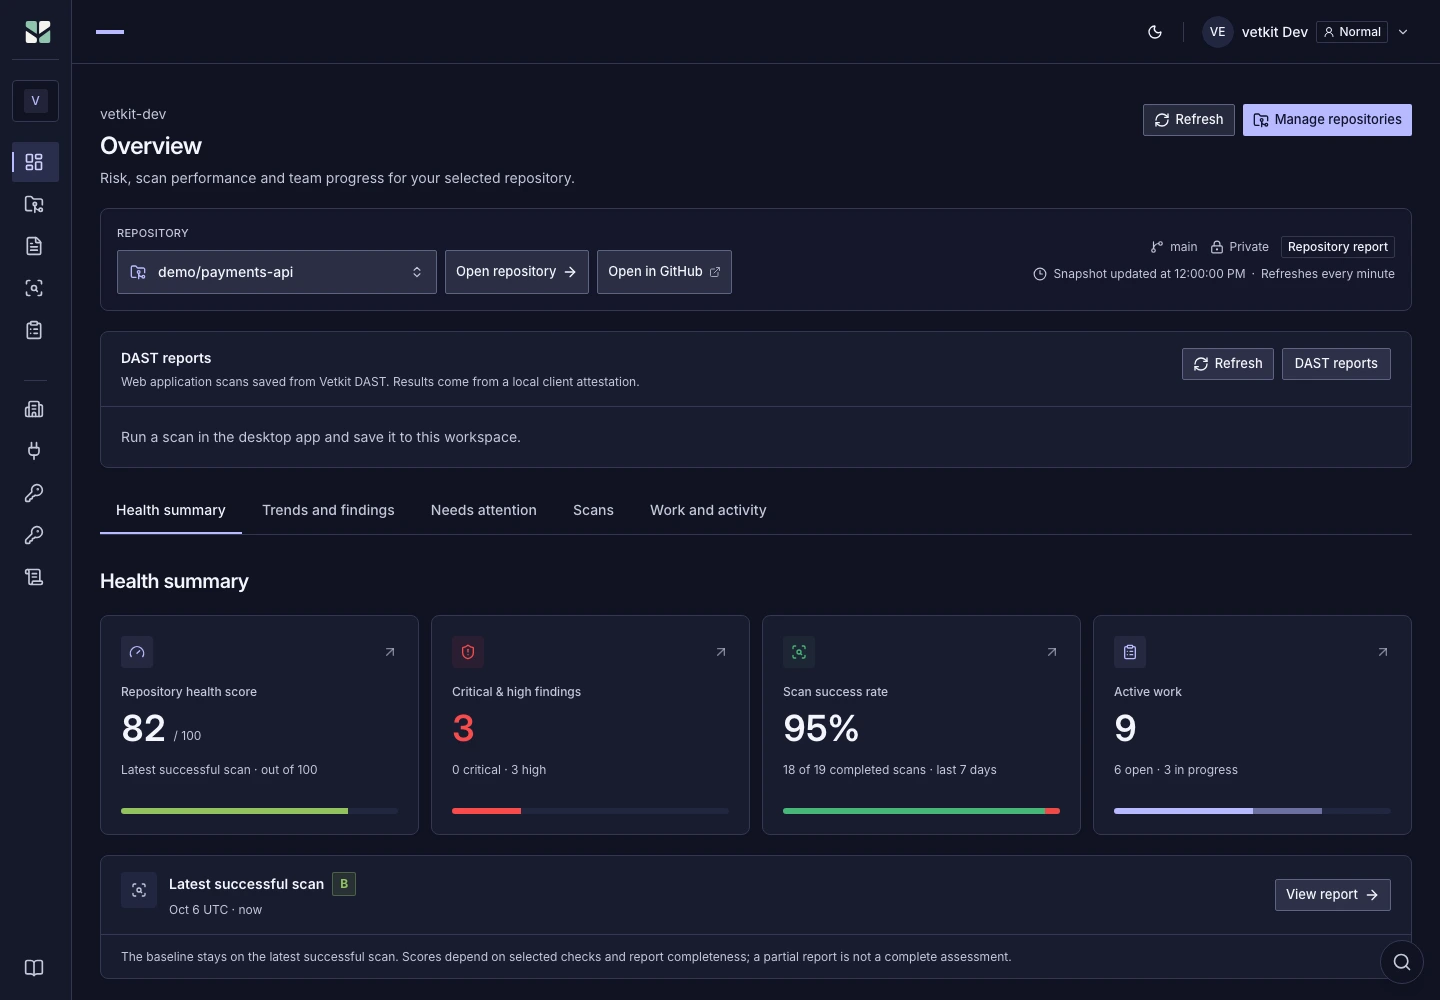
The vetkit overview showing a demo repository’s health score, high-severity findings, scan activity and active remediation work.The vetkit overview showing a demo repository’s health score, high-severity findings, scan activity and active remediation work.
Actual vetkit interface with demo data. Not a customer workspace. Expanded features shown; Free Quick Scan has a limited scope.
Risk, scan activity and work in one view
Grades across five audit suites
Owners, priorities and target dates
Choose individual checks for each audit

Powered by proven open-source engines

  • gitleaks
  • OSV-Scanner
  • Opengrep
  • Trivy
  • zizmor
  • tree-sitter
  • Retire.js
  • Bandit
  • gosec
  • cargo-audit
  • OWASP ZAP

Works withGitHubClaude CodeCodexCursorMCPSARIF

How it works

From repository URL to report in three steps

No agents to install, no pipelines to wire up. Start in the browser; automate later with the API or MCP.

  1. Connect a repository

    Create an account with Google, GitHub, Apple or email, then connect a GitHub, GitLab.com or Bitbucket Cloud repository. For private GitHub code, install the vetkit GitHub App only on the repositories you select; for private GitLab or Bitbucket projects, add an access token or connect the provider. Signing in does not grant repository access.

    GitHub · GitLab.com · Bitbucket Cloud

  2. Run an audit

    Start a Security Quick Scan on the latest default-branch commit. We scan for secrets, known dependency vulnerabilities and basic security posture — without installing, building or executing your code.

    github.com/acme/payments-api @ main

  3. Get a graded report

    An A–F grade overall and per suite, a score per category, and every finding with file, line, severity and a suggested fix. Re-run later to see which findings are new and how many you fixed. Download a PDF report, Markdown or SARIF, or fetch JSON over the API.

    B · 86/100 · 10 findings

AI code risks

Catch the mistakes AI assistants keep making

Coding agents ship fast — and repeat the same failure modes: packages that do not exist, half-finished implementations, missing database security and prompt-injection paths. The AI code risks suite looks for exactly these.

  • Hallucinated packages

    Dependencies and imports that do not exist on npm, PyPI and other public registries — the names attackers register for slopsquatting — plus versions that were never published and packages first released in the last 30 days.

  • Unfinished code

    Stub implementations, “rest of the code” placeholders, mock data and placeholder credentials left in production paths, copy-suffixed duplicate files and blanket type or lint suppressions.

  • App platform pitfalls

    Supabase tables without row level security, secrets exposed through public environment variables, unauthenticated API routes and access checks that only run in the browser.

  • LLM & agent security

    Prompt injection paths, model output reaching code execution, SQL or HTML, LLM API keys in client code, unbounded model calls and risky agent configuration such as hidden instructions or unpinned MCP servers.

See every AI code risk check
Claude Code · vetkit MCP

Audit acme/payments-api for AI code risks and list anything high or critical.

1,284 files read on main · nothing executed

  • CRITICALLLM & agent securitysrc/agent/tools.ts:88
  • HIGHHallucinated packagespackage.json:14
  • MEDIUMApp platform pitfallssupabase/migrations/0001_init.sql:7
  • MEDIUMUnfinished codesrc/billing/refund.ts:41

4 findings with file and line · report ready

Illustrative agent session with sample data. Not a real repository.

What we check

Five suites, one graded report

Run security, code quality, sustainability, AI code risk and production readiness checks together or on their own, and pick individual checks per audit or as a repository default. vetkit combines open-source scanners with its own checks, deduplicates the findings and names every tool version that ran.

01 / 05

Security

What an attacker would look for first: credentials, known-vulnerable packages and code that trusts input it should not.

43% of the overall score

Signals in this suite

  • Secret scanning
  • Vulnerable dependencies
  • Code vulnerabilities
Explore checks & tools
Secret scanning
gitleaks

Cloud, SaaS and payment provider keys, tokens, passwords and private keys committed to the tree.

Vulnerable dependencies
OSV-Scanner

Packages your lockfiles pin, matched against osv.dev — npm, PyPI, Go, crates.io, Maven, RubyGems and more. Malicious packages are critical; actively exploited CVEs (CISA KEV) are ranked up.

Code vulnerabilities
Opengrep · vetkit rules

Selected language-specific rules for injection, unsafe deserialization, weak crypto, disabled TLS checks, SSRF and XSS, plus insecure server, mobile and shell configuration, with CWE references.

Security posture
native

Committed .env files, keystores, cloud and Terraform credentials, database dumps, manifests without a lockfile, no SECURITY.md disclosure policy.

Infrastructure & CI/CD
Trivy · zizmor

Terraform, CloudFormation, Kubernetes, Helm and Dockerfile misconfigurations; GitHub Actions script injection, over-broad tokens and pwn requests.

Supply chain & outdated software
native · Retire.js · endoflife.date

Lockfile injection, risky install scripts, Trojan Source, vendored vulnerable libraries and end-of-life runtimes or base images.

  • Secret values are redacted — only a one-way hash tracks a finding across audits
  • A repository cannot hide findings with its own scanner config files or inline ignore comments
AI-authorship signal
Beta · not scored

AI-authorship signal

An optional check in the AI code risks suite: a heuristic estimate of how much of a codebase was written with AI assistance, based on metadata at the end of commit messages (commit trailers) and commit cadence, agent configuration files such as CLAUDE.md or AGENTS.md, and a model review of a small sample of files.

Honest caveat: AI authorship cannot be reliably detected from code. This is a signal, not evidence — a conversation starter. It is informational only and never affects your grade.

How grading works

Each category starts at 100 and loses points per finding, weighted by severity and capped per severity so a pile of minor findings cannot sink a repo. Categories roll up into a grade per suite, and the suites that ran into an overall score. Checks and suites you skip are left out, not counted as perfect: their weight is shared among the ones that ran.

A
≥ 90
B
≥ 80
C
≥ 70
D
≥ 60
F
< 60

An unresolved critical finding caps the grade at D, and the report tells you why. Suppress false positives with a reason and an optional expiry; suppressions carry over to later audits and stay visible in the audit trail.

By the numbers

Depth you can verify

Every number here comes from the product itself: the suites, checks and engines that appear in your report.

audit suitesSecurity, quality, sustainability, AI risks and production readiness
5
check familiesFrom secret scanning to N+1 queries
24
languages with code rulesPlus dependency ecosystems and repository-wide checks
11
open-source enginesEvery tool version is named in the report
11
report formatsPDF, Markdown, SARIF and JSON
4

Solutions

Built for everyone accountable for shipping

Founders, engineering teams, security reviewers and AI-assisted developers read the same evidence — each from the angle they need.

Founders & builders

Ship AI-built products without shipping their blind spots

Get an independent second look before a launch, an investor review or your first enterprise customer — without hiring a security team first.

  • Start with a free Security Quick Scan of your default branch
  • Find leaked keys and known vulnerable dependencies in minutes
  • Spot AI-specific mistakes such as hallucinated packages or tables without row level security
  • Share a graded PDF report with partners and customers

Engineering teams

Turn findings into work with owners and deadlines

Keep risk visible across repositories and make sure every important finding has someone responsible for it.

  • Assign findings with priorities and target dates
  • Compare audits to see what is new and what you fixed
  • Follow open, in-progress and resolved work per repository
  • Team organizations with owner, admin, member and viewer roles

Security teams

Review evidence, not another opaque AI verdict

Every finding has a file, a line, a severity and the tool version that produced it, so decisions can be checked and repeated.

  • Risk acceptance and false positives need a reason and an independent review
  • Accepted risks expire instead of disappearing for good
  • SARIF export for GitHub code scanning, plus an audit log
  • Read-only audit tokens, ephemeral checkouts and redacted secrets

AI-assisted development

Close the loop between generating and verifying code

Connect Claude Code, Codex, Cursor or any MCP client, and let the agent run audits, read findings and confirm its own fixes.

  • MCP server for any stdio-capable client
  • Scoped API keys for CI and automation
  • Findings with file, line and a suggested fix
  • Re-run audits to confirm what the agent fixed

MCP & API

Let your coding agent check its own work

The vetkit MCP server gives any stdio-capable MCP client tools to connect repos, run audits and read findings. Everything in the app is also available over a documented REST API.

  1. 01Build with your agent
  2. 02Audit the repository
  3. 03Prioritize, assign, re-check
  • Audit acme/payments-api on main and summarize anything high or critical.
  • Which dependencies in the last audit have a fixed version available?
  • Compare this audit with the previous one — what did we fix?
  • GitHub
  • Claude Code
  • Codex
  • Cursor
  • REST API
  • MCP
MCP · stdio
{  "command": "npx",  "args": [    "-y",    "@vetkit/mcp"  ],  "env": {    "VETKIT_API_KEY": "<your-api-key>"  }}
REST API
# Start an audit on a connected repositorycurl -X POST https://api.vetkit.dev/v1/orgs/$ORG_ID/audits \  -H "Authorization: Bearer $VETKIT_API_KEY" \  -H "Content-Type: application/json" \  -d "{\"repositoryId\":\"$REPO_ID\",\"ref\":\"main\"}" # Download the report as SARIF for GitHub code scanningcurl "https://api.vetkit.dev/v1/orgs/$ORG_ID/audits/$AUDIT_ID/report?format=sarif" \  -H "Authorization: Bearer $VETKIT_API_KEY" -o vetkit.sarif

Security & privacy

A code auditor should be the least risky thing you connect

We built vetkit around least privilege and short retention, because you are trusting it with your source.

  • Read-only audits

    Each audit reads only the repository you grant, with a read-only token. The GitHub App writes only for features you turn on or start — PR Delta Review checks and comments, fix pull requests on a new branch, and GitHub issues you create from a finding. It cannot change settings or touch other repos.

  • Your code is never executed

    No install scripts, builds or tests. Analyzers only read files, symlinks are disabled at checkout, and a repo’s own scanner config is ignored.

  • Ephemeral checkouts

    Each audit uses a shallow clone in a fresh temporary directory that is deleted when the audit finishes — pass or fail.

  • Secret values are never stored

    Secret findings are redacted before they are saved. We keep the file, line and a one-way hash — never the credential itself.

  • Short-lived, unpersisted tokens

    GitHub access tokens are minted per audit, scoped to that one repository, expire within an hour and are never written to disk or database.

  • Hashed credentials

    Session tokens and API keys are stored only as hashes. An API key is shown exactly once, carries explicit scopes and can be revoked instantly.

GitHub App permissions

Exactly what the app requests. GitHub will ask you to approve any change.

Permissions requested by the vetkit GitHub App
PermissionAccess
ContentsFetch the files at the audited commit; write only to open a fix pull request you startRead and write
MetadataList repositories and default branchesRead
Pull requestsPR Delta Review comments, /vetkit commands and fix pull requestsRead and write
ChecksPublish the PR Delta Review result as a check runRead and write
IssuesCreate a GitHub issue from a finding when you choose to, and check the status of linked issuesRead and write
Email addressesIdentify your account at sign-inRead

More detail on our security page and in the privacy policy.

Enterprise / on-premise needs

Need vetkit in your own infrastructure?

Tell us about your deployment environment, security requirements, and integrations. We’ll assess the fit and discuss the scope and next steps.

Discuss enterprise needs

Tools

See what happens beyond the code.

A repository audit shows one side of the story. Capture browser traffic with the Chrome extension, scan a running application with VetKit DAST on desktop, and keep audit findings in front of you in VS Code.

Each tool produces its own report, with a clear scope and evidence your team can act on.

VetKit Network MonitorAccess by request

See what the browser actually loads.

Monitor a tab you choose and surface failed, slow, repeated and oversized requests without reading request or response bodies.

01Live triage
Filter requests and prioritize the issues that affect the page.
02Before and after
Save local snapshots and compare results for the same domain.
03Portable reports
Export JSON or CSV; save to your VetKit account only with your approval.

Only the selected tab is monitored. Request and response bodies are never read.

Ask about the Chrome extension
Illustrative product view · Chrome
example.com
VetKit Network MonitorMonitoring

Network report

Selected tab

example.com

Requests

148

Findings

09

Measured size

3.4 MB

Priority signals

  • Slow request/api/search
  • Repeated call/api/search
  • HTTP 5xx/api/cart
Snapshot comparisonBefore 1.8sAfter 1.1s

Open network analysis

VetKit DASTAccess by request

Test the application that is running.

Run an OWASP ZAP scan against a web application, then bring a scoped security summary into your VetKit workspace.

01Guided scans
Choose a target and scan mode in the desktop app.
02Risk-led review
Review ZAP rules by severity, confidence and occurrence count.
03Shareable evidence
Open the report in your workspace and export a DAST PDF.

The uploaded summary contains target origins and aggregated rule results, without request paths, headers or bodies.

Ask about the desktop app
Illustrative product view · Desktop
VetKit DASTOWASP ZAP

New scan · on this computer

Target URL

https://app.example.com

Run scan

Scan mode

PassiveFullCustom

OWASP ZAP runs locally

DAST report

Scoped target

app.example.com

High

02

Medium

04

Low

01

Accepted rules
ZAP ruleRiskOccurrences
ZAP 10020Medium04
ZAP 10038Medium02

PDF report available in the workspace

VetKit for VS CodeAccess by request

Bring audit findings into your editor.

See the latest VetKit audit for the repository you have open as inline diagnostics and in a Findings view, without leaving VS Code.

01Inline diagnostics
Findings appear on the lines they point to, with severity and the analyzer that found them.
02Findings view
Browse findings by suite in the VetKit activity bar and jump straight to the code.
03Commit-aware
Results are marked stale when your local HEAD differs from the audited commit.

Sign in from the browser with a one-time code. The extension uses a read-only key and never uploads source code.

Ask about the VS Code extension
Illustrative product view · VS Code
acme/apisrc/db.ts
import { Pool } from 'pg';
export const db = new Pool({
host: 'db.internal',
password: 'pg_live_9f2c…',
});
export async function findUser(id) {
const sql = `SELECT * FROM users WHERE id = ${id}`;
return db.query(sql);
}

High · Hard-coded secret

A database password is committed in source. Move it to an environment variable and rotate it.

vetkit · gitleaks

VetKit · 5 findings · latest audit

VetKit Agent WatchAccess by request

See what your AI coding agents actually do.

Agent Watch runs on the developer’s machine and reports when Claude Code, Codex, Cursor and other agents read credentials, reach new domains, delete files or change their own settings.

01Grouped alerts
Rule-based alerts with severity, tool and device; repeats stay one item.
02Session attestations
Each session states what the agent did not do, with the sensor coverage behind it.
03Agent posture
Review bypass modes, broad permissions and MCP servers across your team’s machines.

Uploads are metadata only: alerts, session summaries and posture, never file contents or prompts. Raw events stay on the device unless the organization and each user opt in.

Ask about Agent Watch
Illustrative product view · Agent Watch
VetKit Agent WatchWatching

Session summary

Claude Code on acme/api

Alerts

  • Read of cloud credentialsHigh
  • First connection to a new domainMedium

Attestations

  • No reads outside the projectVerified
  • Egress only to listed domainsPartial

Languages & coverage

Your stack. Clear coverage.

Review projects across popular programming languages. See which code checks are available for your stack before you scan.

Current expanded-scan capabilities
LanguageCode securityComplexity & duplication
JavaScript / TypeScriptSelected rulesAvailable
PythonSelected rulesAvailable
JavaSelected rulesAvailable
C#Selected rulesAvailable
GoSelected rulesAvailable
PHPSelected rulesAvailable
RubySelected rulesAvailable
RustSelected rulesAvailable
C / C++Selected rulesAvailable
KotlinSelected rulesAvailable
SwiftSelected rulesAvailable

Checks across repositories

Secret scanning, basic security posture and repository hygiene inspect supported files without depending on one source-code language.

Dependency ecosystems

Known vulnerabilities are checked through the manifest and lockfile formats supported by OSV-Scanner, including npm, PyPI, Go, Cargo, Maven, NuGet, Bundler and Composer.

Additional language checks

Python: Bandit. Go: gosec. Rust: cargo-audit with Cargo.lock. These checks require the relevant scanner to be installed and selected.

This table describes the checks available in a full scan. Free Quick Scan covers only secrets, known dependency vulnerabilities and basic posture. Coverage varies by framework, inputs and tool availability; reports show checks that ran, skipped or failed.

Pricing

Every feature included. No plans to pick.

Every account gets the whole platform. Quick Scan is free every month; a full scan uses one credit. A quick scan is not a complete security audit or a guarantee that your app is secure.

01 / Free Security Quick Scan

Security Quick Scan

$0

Google, GitHub, Apple or email · No AI in the free scan

  • Secrets, known dependency vulnerabilities and basic security posture
  • 10 scans per owner per calendar month · 50 MB of indexed input · 5,000 files · 3-minute limit
  • All detected findings are visible, including critical issues. The default branch's latest commit only; no git history or automatic scans.
Scan your repo for free

02 / Full scan

Go deeper when you need it.

1 credit

Any branch, tag or commit and any checks: deep SAST, secret history, language-specific rules, code quality, sustainability, AI code risks and production readiness, plus media files and optional AI review with your own provider key. Uploading a DAST report also uses one credit.

New accounts get 3 starter credits. Need more? Request credits in the app.

Each friend you invite adds one more credit. Credits do not expire, have no cash value and are never charged automatically.

  • Grades across five audit suites
  • Owners, priorities and target dates
  • Choose individual checks for each audit
Talk to us about your team

Every account includes AI review, triage and fixes with your own LLM key, integrations, ChatOps, plugins, automatic scans, Agent Watch and multiple workspaces. Automatic scans are off until you turn them on, and each one uses a credit. Quick Scan never sends your source code to an AI model.

FAQ

Questions, answered plainly

Something missing? Email contact@vetkit.dev.

How do I get access?
Create an account to start a free scan. Connect a public or private repository from GitHub, GitLab.com or Bitbucket Cloud, review the scope and start the scan. No invitation is required. New accounts also get starter credits for full scans, and you can request more credits in the app.
Do you run my code?
No. vetkit never installs dependencies, runs build scripts or executes tests. Every analyzer reads files from a shallow checkout; nothing from your repository is ever executed.
Do you store my source code?
No. The checkout lives in a temporary directory that is deleted as soon as the audit finishes. We store the findings: rule, file path, line numbers and a short snippet (up to 1 KB) around the issue so the report is useful. Snippets for secret findings are redacted.
What happens when you find a secret?
The value is redacted before anything is saved. We keep a one-way hash so the same secret can be recognized in later audits without ever storing it. You should still rotate any credential that was committed — git history keeps it even after you delete the file.
What access does the GitHub App need?
Read access to contents and metadata on the repositories you select, plus your email address at sign-in; every audit uses a read-only token for one repository. Write access to contents, pull requests, checks and issues is used only for features you turn on or start: PR Delta Review results and comments, fix pull requests opened from a new branch, and GitHub issues you create from a finding. If an installation has not yet approved write access to issues, only the Create GitHub issue action is disabled. See the permissions table.
Which languages and ecosystems are supported?
See the language coverage table for code-security rules and complexity and duplication analysis. Support varies by language and check. Secrets and basic posture checks inspect supported repository files; dependency scanning follows the manifest and lockfile formats supported by OSV-Scanner. Every report shows which checks ran, skipped or failed.
What does the sustainability suite tell me?
Whether the code can keep being shipped and maintained. It flags dependencies whose license (GPL, AGPL, restricted-use or unknown) conflicts with how your project is licensed, direct dependencies that are deprecated or far behind their latest release, and maintenance risks visible in the commit history, such as a repository nobody has touched in a year or one that depends on a single contributor. To do this, package names and versions from your lockfiles are looked up on osv.dev and deps.dev; no source code is sent. License findings are a starting point for review, not legal advice.
How reliable is the AI-authorship signal?
Treat it as a hint, not a verdict. AI authorship cannot be reliably detected from code, so the signal is labelled beta, shows its evidence and caveats, and never affects your grade. When it runs, a small sample of files is sent to an AI model provider for analysis — see the privacy policy for details.
Can I use vetkit from CI or my coding agent?
Yes. Create an API key with only the scopes you need, then use the REST API from any pipeline or install the MCP server in Claude Code or another MCP client. Reports export to SARIF 2.1.0 for GitHub code scanning.
How do I delete my data?
You can delete individual audits in the app, disconnect a repository, and uninstall the GitHub App from your GitHub settings at any time. Owners can delete a team organization with all of its data under Workspace settings → Organization by typing its slug to confirm: access ends immediately and the data is permanently removed after 30 days. Personal organizations are removed when your account is deleted. To delete your account, email privacy@vetkit.dev and we will take care of it within 30 days.

Get a second pair of eyes on your next release.

Create an account, connect your GitHub, GitLab or Bitbucket repository and get your first security report. All detected findings stay visible — even the critical ones.

  • Free Security Quick Scan
  • No automatic charges
  • Read-only audit access

Prefer to write directly? contact@vetkit.dev

Request early access

Tell us a little about your team and the repositories you want to audit. We onboard teams in small batches and will reply by email.

We use these details only to reply to your request. Privacy policy